Nobody was in charge
Arguing over whether the NIKKE launcher stealer was Shift Up's fault or Level Infinite's misses the point: in the crisis nobody took the chair, and the empty chair is what turned a breach into chaos.
"It's not Shift Up's fault, it's Level Infinite's." "It's Tencent's launcher." "They were probably asleep." That is what my replies looked like on 4 November, and it is the argument everyone wanted to have.
It is the wrong argument. Whose fault the breach was is a question for the post-mortem. The question during the crisis was who was in charge. The answer was nobody. And that empty chair did more damage than the files did.
This was a stealer, on the official launcher, for five weeks
Four files on NIKKE's own CDN were changed on 27 September. From late October, on some launches and not others, the launcher used its own signed downloader to install an agent and a DLL that loaded into every Chrome-based app on the PC. It took browser passwords, session cookies, Windows' saved logins and 28 crypto wallets. It took screenshots and files. While the launcher was open, the attacker could run commands on your machine.
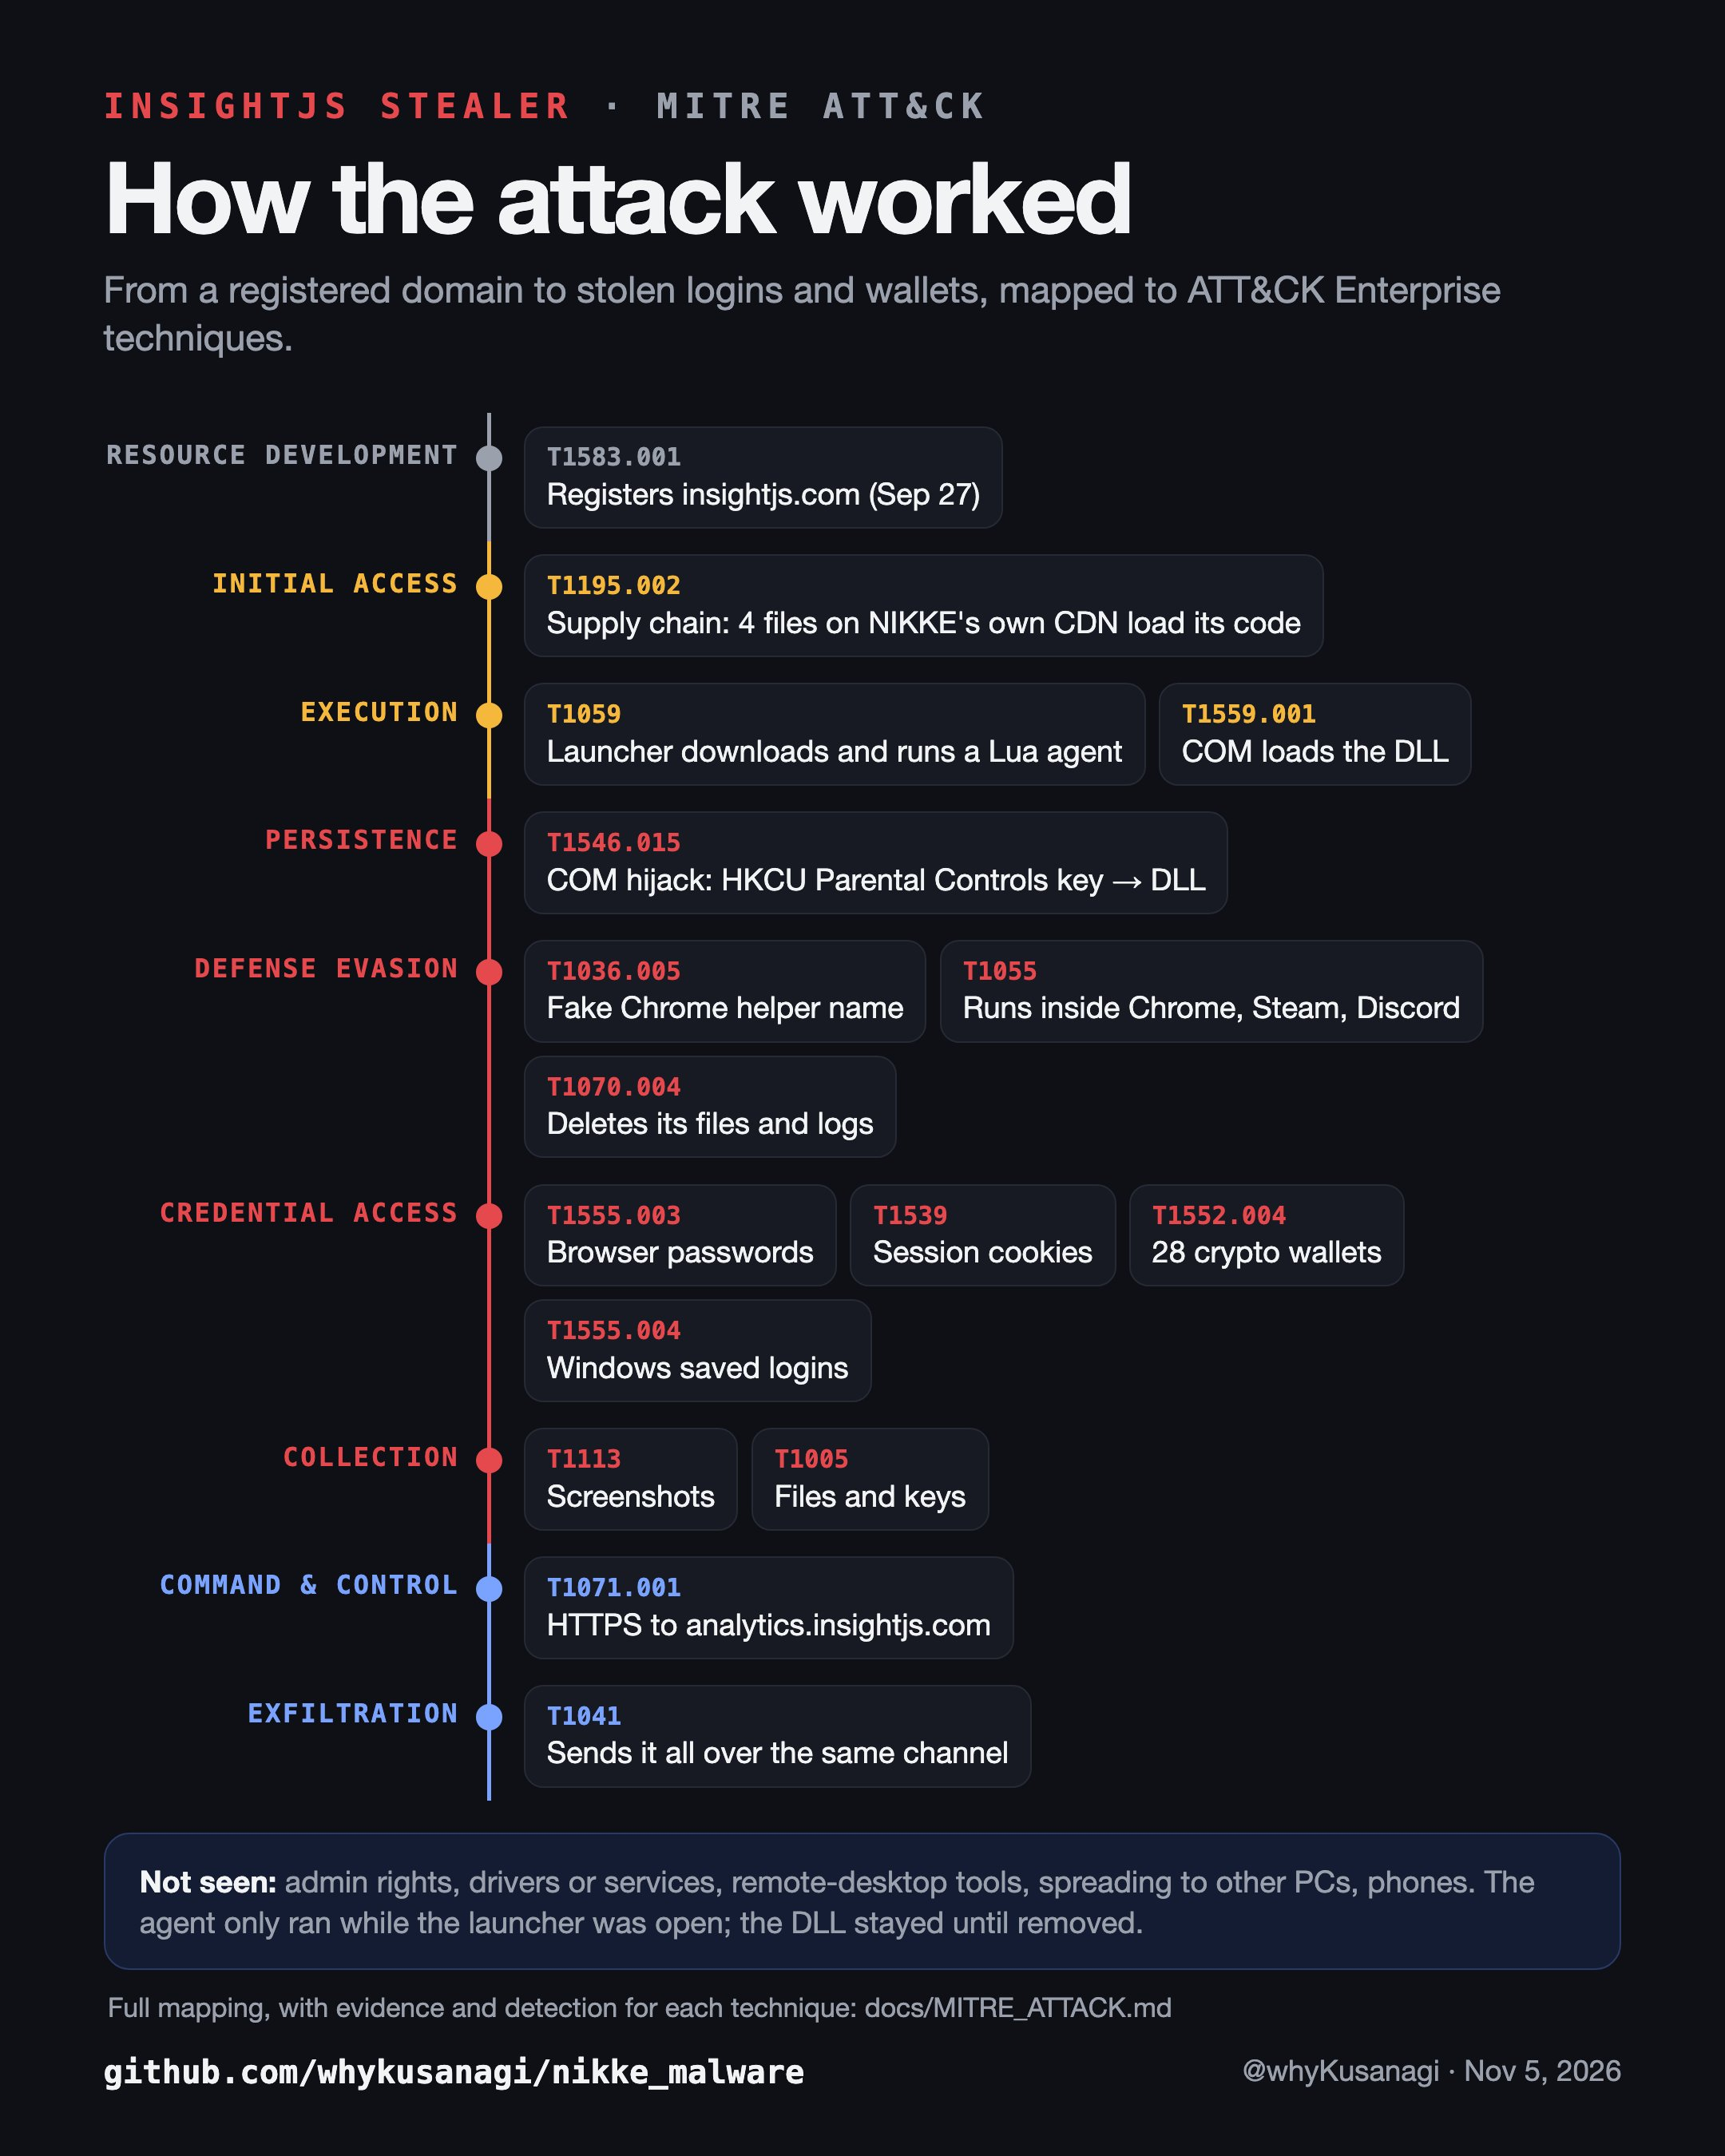
That sets the clock. A stolen seed phrase gets emptied in minutes. A stolen session cookie walks straight past your password and your 2FA. From the moment the company knew, every hour without a clear instruction was an hour in which somebody's financial safety and stability came closer to being ruined for certain.
Look at which column is full
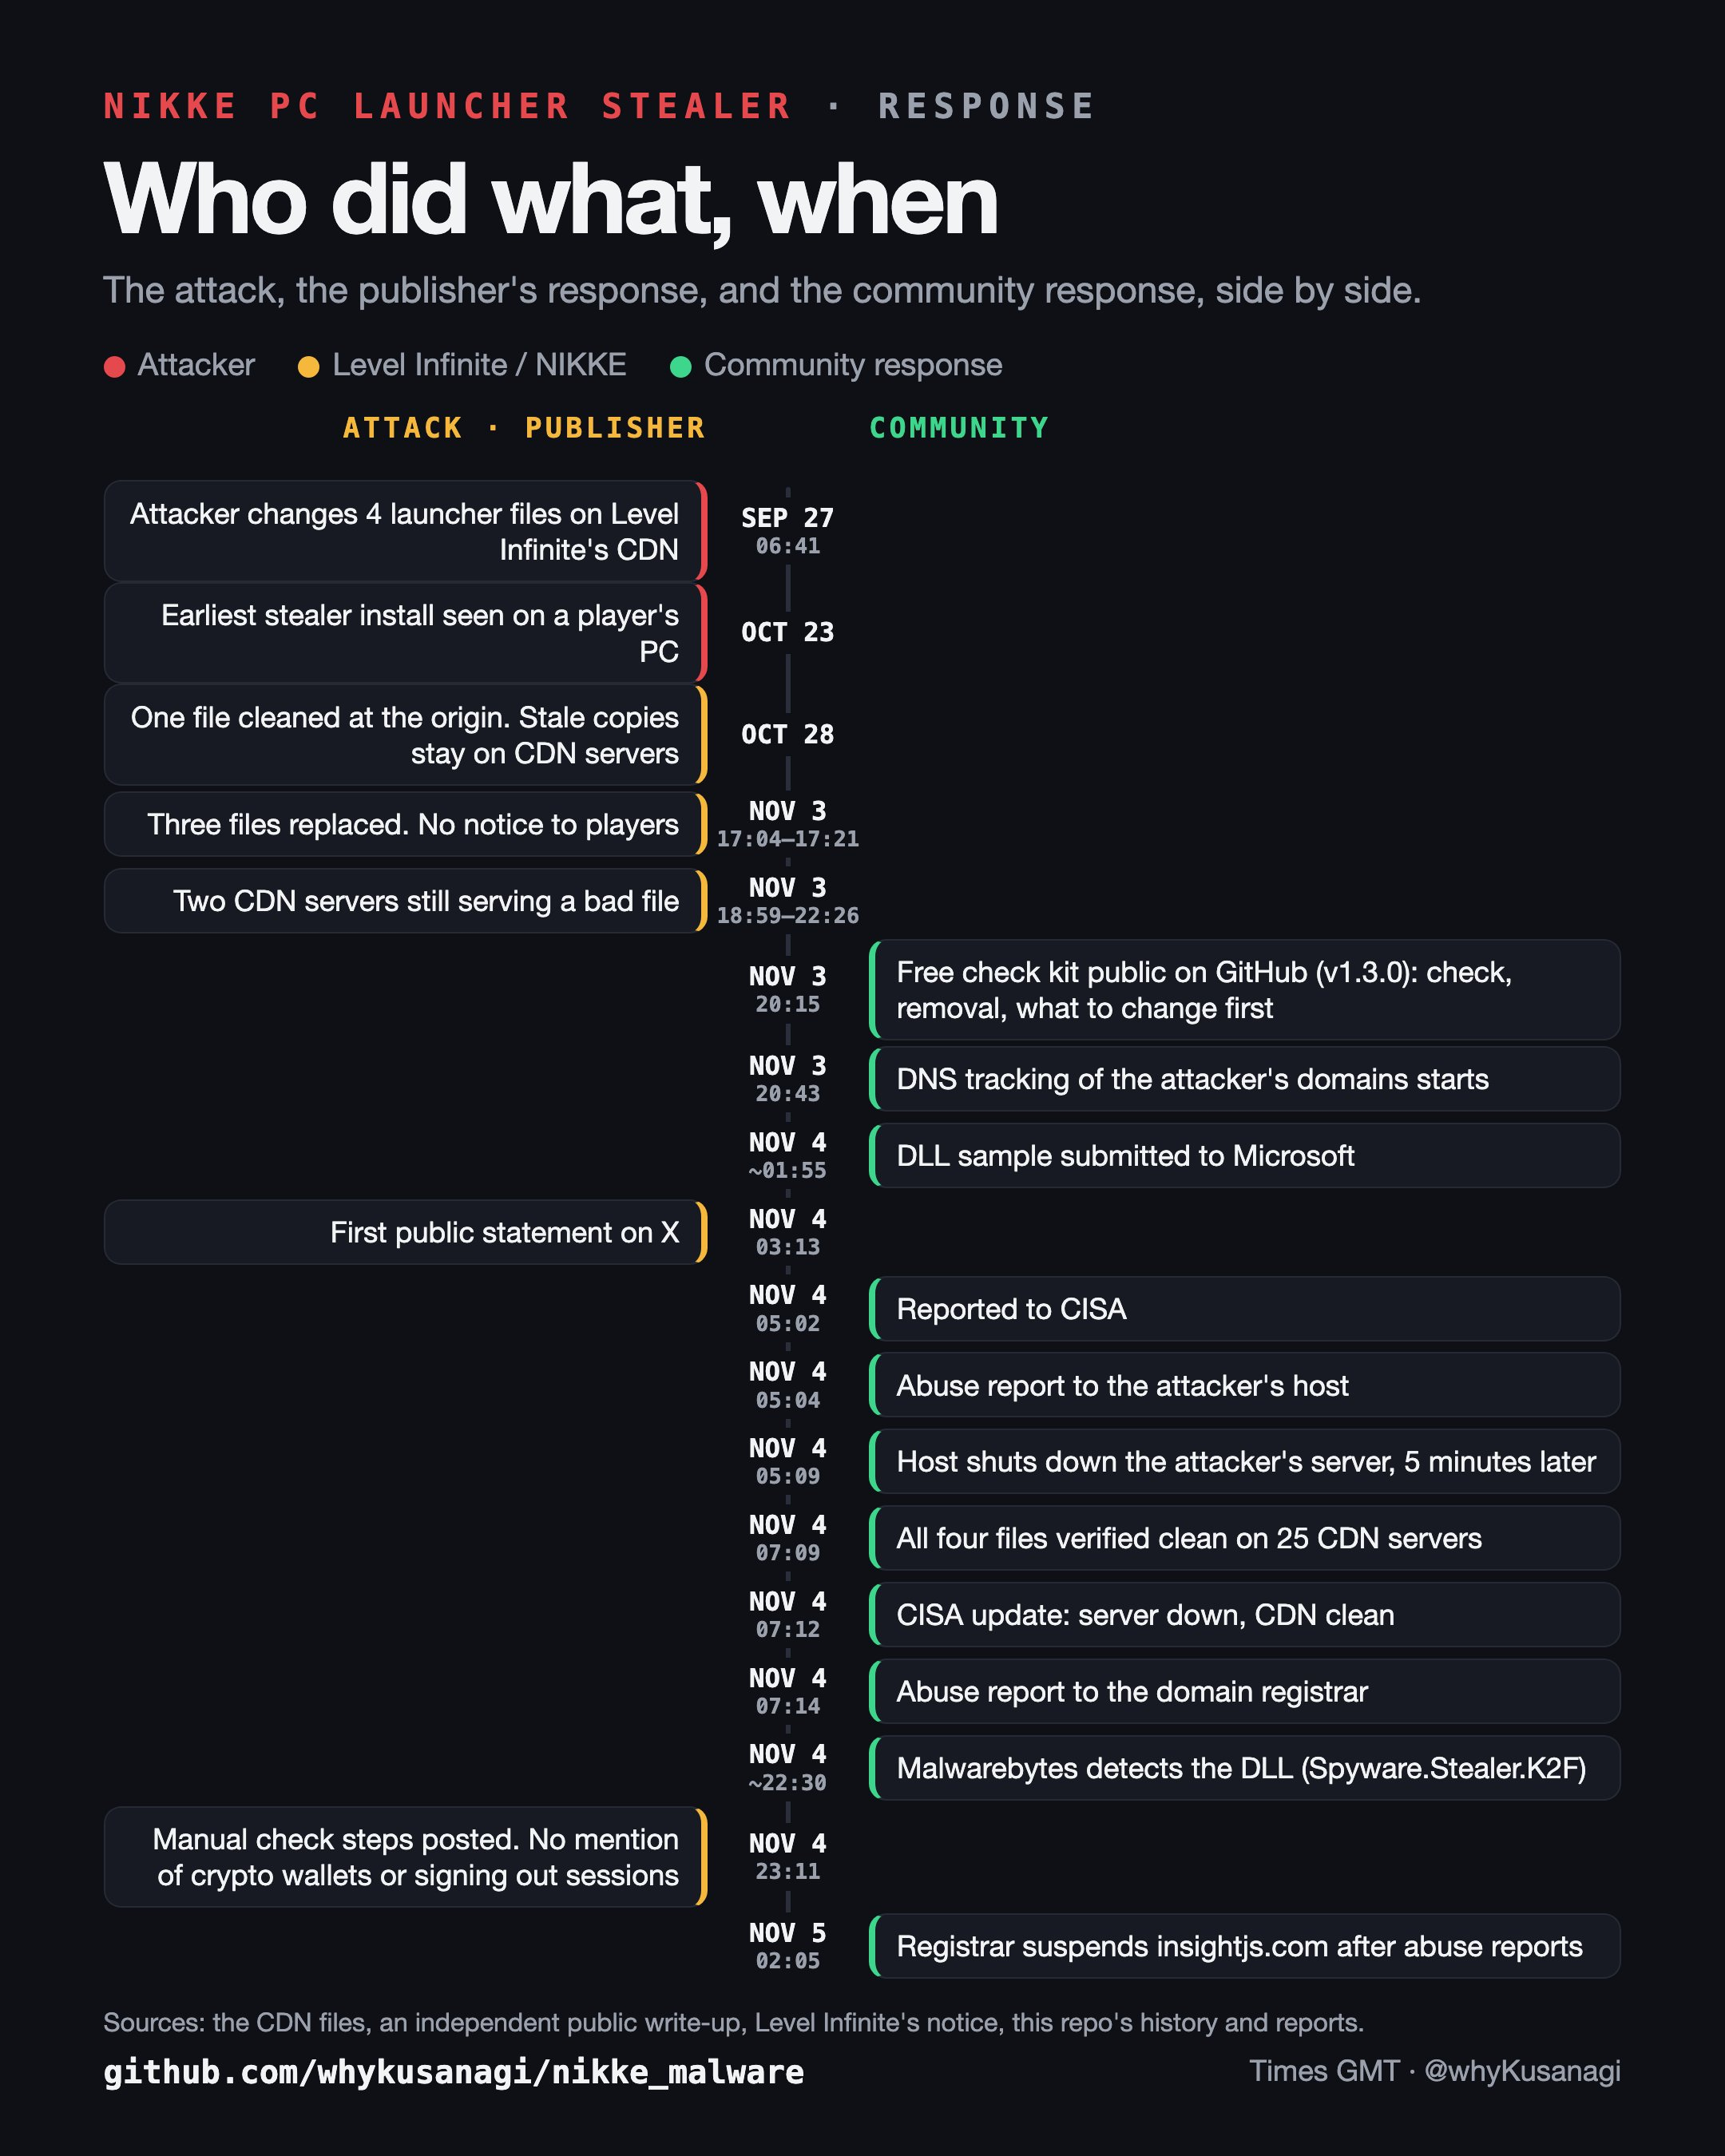
The left column is the attacker and the publisher. The right column is everyone else. Read it once and the whole post is there.
- 3 Nov, 17:04. Level Infinite replaces three of the files. No notice to players. They knew.
- 3 Nov, 20:15. A free check-and-removal kit is public, with what to change first.
- 4 Nov, 01:55. The DLL sample goes to Microsoft.
- 4 Nov, 03:13. The first official word, ten hours after the fix: an "anomaly".
- 4 Nov, 05:02 to 07:14. Reported to CISA. Abuse report to the attacker's host, which pulls the server five minutes later. All four files verified clean on 25 CDN servers. Abuse report to the registrar.
- 4 Nov, 23:11. Official manual check steps. No mention of crypto wallets, or of signing out of sessions.
The right-hand column is mine and a handful of other people's. None of us owns the launcher.
Cover first, care later
There is a playbook for this, and anyone who has watched a large company in trouble has seen it run. Here it is, with what each step looked like this week.
In Korea and Japan the last step has a familiar picture: executives bowing in front of cameras. Everywhere else it is a press release. The order never changes. It is the instinct of a war room or a political crisis, where everyone's first move is to protect their own position and every sentence is a potential admission, so every sentence comes out late and vague. That is face-saving. It is designed to save the company, not the players.
Here is what it sounded like. Ten hours after they had already swapped the files:
We have identified an issue indicating that the PC Launcher's script files may have been tampered with by a third party. … We apologize for the inconvenience caused.
"Anomaly." "May have been." "Inconvenience." It does not say a stealer ran. It does not say change anything. And people were waiting for exactly that post before they believed any of it. People in my own chat said it plainly: a lot of players did not believe any of it was real until the studio posted. So the one voice everyone trusted used its first words to say "relax".
Even the step up was empty
Five hours later, Shift Up's CEO stepped in. Kim Hyung-tae quoted the anomaly notice on the Japanese account at 08:06 GMT and on the English one at 08:07, with the same statement in each language. Same approved text, same damage control. The English version:
We are currently experiencing issues related to the PC launcher. In collaboration with LEVEL INFINITE, we are dedicating all our resources to identifying a fundamental solution, and we are also preparing follow-up measures. We sincerely apologize for the concern and inconvenience this has caused you, Commanders.
This was the moment. The man at the top of the studio, with more than seven hundred thousand views across those two posts alone, could have said four things: a stealer may have run on your PC, move your crypto, change your passwords from another device, sign out of every session. Instead: "issues", "collaboration", "all our resources", "inconvenience". It is a leader's voice with nothing in it. It looks like stepping up, and it tells nobody what to do.
I replied twenty minutes later.
More empty promises, the people that whistleblew about the cheaters and hackers all got axed or thrown under the bus. You are looking for a sacrifical lamb to offer to the community once again. Typical saving face behavior we've come to expect from the leadership team at Shift Up. The NIKKE community had to offer solutions to help people protect their computers while Shift Up, Tencent, and Level Infinite sat on their asses for about 12 hours. I have filed a report with CISA, and will be filing additional breach reports with US Agencies. I reccomend players in the EU file with the European Commission since you guys can't seem to get your story straight and will point fingers at each other.
Sharp, and I stand by the core of it. The replies underneath went straight to the defence this post is about. "It wasn't even their fault to begin with." "It's not their fault what happened to a third party launcher." "It's Tencent / Level Infinite who fucked up." "They can't solve the issue in 10 min."
Nobody asked them to solve it in ten minutes. The ask was to say what to do. That takes one sentence, and it was the one sentence nobody in charge would write.
Three parties means nobody's job
Shift Up makes the game. Level Infinite publishes it and runs the launcher and the CDN. Tencent owns Level Infinite, and the files were served from Tencent's storage. Fans hear that and conclude it is not Shift Up's problem. It is the opposite. Three parties is exactly how a crisis becomes nobody's job.
They can point to Level Infinite. They can point to Tencent. Tencent is going to point to somebody else. They're going to be like, oh, it's some contractor who did something. He was asleep. They didn't scan some package.
The developer waits for the publisher. The publisher waits for legal. The parent company says nothing at all. Each wait is defensible. Together they are an empty chair. Someone in my chat put the rule in seven words during that stream: "first rule of leadership: everything's your fault". The leader is whoever acts as if it is their fault before anyone has worked out whose fault it is.
Players do not see three companies. They see one game, one launcher, one logo, and a CEO who speaks for the studio. "It's not Shift Up, it's Level Infinite" is an org chart. It is not an answer to "what do I do about my wallet?"
An empty chair gets filled, and it gets filled with chaos
A vacuum does not stay empty. A player in an NGA forum thread found the stealer, because League's anti-cheat refused to start with the DLL loaded. An independent researcher tore down the CDN files. A stranger registered the attacker's backup domain and turned it into a warning page. None of them was responsible. All of them were filling the chair.
Some of what fills it is good. Some of it is wrong. With no authoritative voice, the biggest account in the room becomes the authority. Sky and Ada told people the registry key in the official steps was one user's key, copied by mistake. It was not. It is Microsoft's fixed ID for Windows Parental Controls, hard-coded into the stealer, the same on every infected PC. Then the posts were deleted rather than corrected, which does nothing for anyone who already acted on them.
This is the key the stealer writes, from the analysis of an infected PC. The ID is the same everywhere; only the folder name changes, because it is the DLL's own hash.
%LOCALAPPDATA%\Google\Chrome\User Data\PlatformExperienceHelper\<64-hex>\platform_experience_helper.dll
HKCU\Software\Classes\CLSID\{E77CC89B-7401-4C04-8CED-149DB35ADD04}\InprocServer32 = <that path>

# {E77CC89B-...} = CLSID_WindowsParentalControls. Every Chromium app asks for it at startup.
# HKLM copy (most installs) -> System32\wpc.dll. Legitimate. Leave it alone.
# HKCU copy -> a browser User Data folder. That is the hijack.
The checker in the kit hard-codes exactly one value for it, because there is only one: $HijackClsids = @('{E77CC89B-7401-4C04-8CED-149DB35ADD04}').
The most damaging advice was not wrong technical detail. It was being told there was nothing to act on yet, during the exact window the stealer was live. At 18:36 GMT on 3 November, Springz (@SpringZ_FSG), not a big account, posted this and the algorithm carried it to nearly half a million views:
Everyone, let's slow down for a second. The Nikke PC "supply chain attack" has ZERO official confirmation. Not from Level Infinite. Not from Shift Up. Nothing. What it does have: one PC. A few screenshots. A string to search for in a log file. No malware sample. No file hashes. No technical proof anyone can verify.
Look at the timing. Level Infinite had already replaced three of the tampered files ninety minutes earlier. MotherSphere's teardown was public. The DLL was on VirusTotal. "Zero official confirmation" was true only because the officials were not talking, and that is exactly the gap someone should not be teaching people to wait in. X's readers added the correction underneath:
Multiple independent analyses confirm modified official Level Infinite CDN files for the NIKKE PC launcher since Sep 2026, enabling a remote access tool with specific IOCs like "k2f_chan" logs; no official statement from Shift Up or Level Infinite.
Community Note on the post above.
I answered it eighty minutes later, less politely than I would now.
whyKusanagi, quoting Springz's "let's slow down" post: calls it the Shift Up defence force at work, says the DLL is already on VirusTotal, that many of the people looking at it work in security, and that the DLL was touching things it should not on enough players' PCs that it was clearly harvesting data to a command-and-control domain. 3 November 2026, 19:58 GMT.
whyKusanagi on X
The guide that followed is careful about one thing, and it deserves the credit: it labels every claim by where it came from. But look at what it is. A line-by-line check of MotherSphere's write-up and the comments under it, prepared with Claude, re-running only what anyone can look up: domain records, certificate logs, DNS. No sample, no teardown, no tool. Its account steps were sound. Its headline instinct stayed the same: a clean log did not justify wiping Windows, wait for the official guidance, and by the evening of 4 November, follow the publisher first.
Reviewing someone else's work is fine. If Unit 42 had checked MotherSphere's analysis or mine, I would welcome it, because that review carries a track record. Nothing here shows a security background. It is a person with an LLM confirming what was already public, and that is not a value add. It is an amplifier.
That is not a personal failing. It is what a vacuum does. When nobody official is speaking, X decides who is, and it picks on reach, not on quality. A guide that tells half a million people to hold still for the publisher, while the publisher is silently patching and saying nothing, sounds responsible. It is the empty chair giving advice, in someone else's voice.
That is the chaos. Not panic for its own sake. Thousands of people trying to protect themselves with a mix of good instructions and bad ones, and no way to tell which is which, because the one voice that could have settled it was saying "inconvenience".
I never asked for the chair
I did not set out to run incident response for a game I play. It started where it should: making sure my own machines were safe. Then my union. Players in my circle were reporting it to me, asking what to do, and trusting me to help more than they trusted any of the three companies.
Then it spread past my circle. Unions I compete against were in my DMs asking for advice, then passing it on to their own members. And then a player on X shared this: a Japanese community moderator, pointing players at the kit.
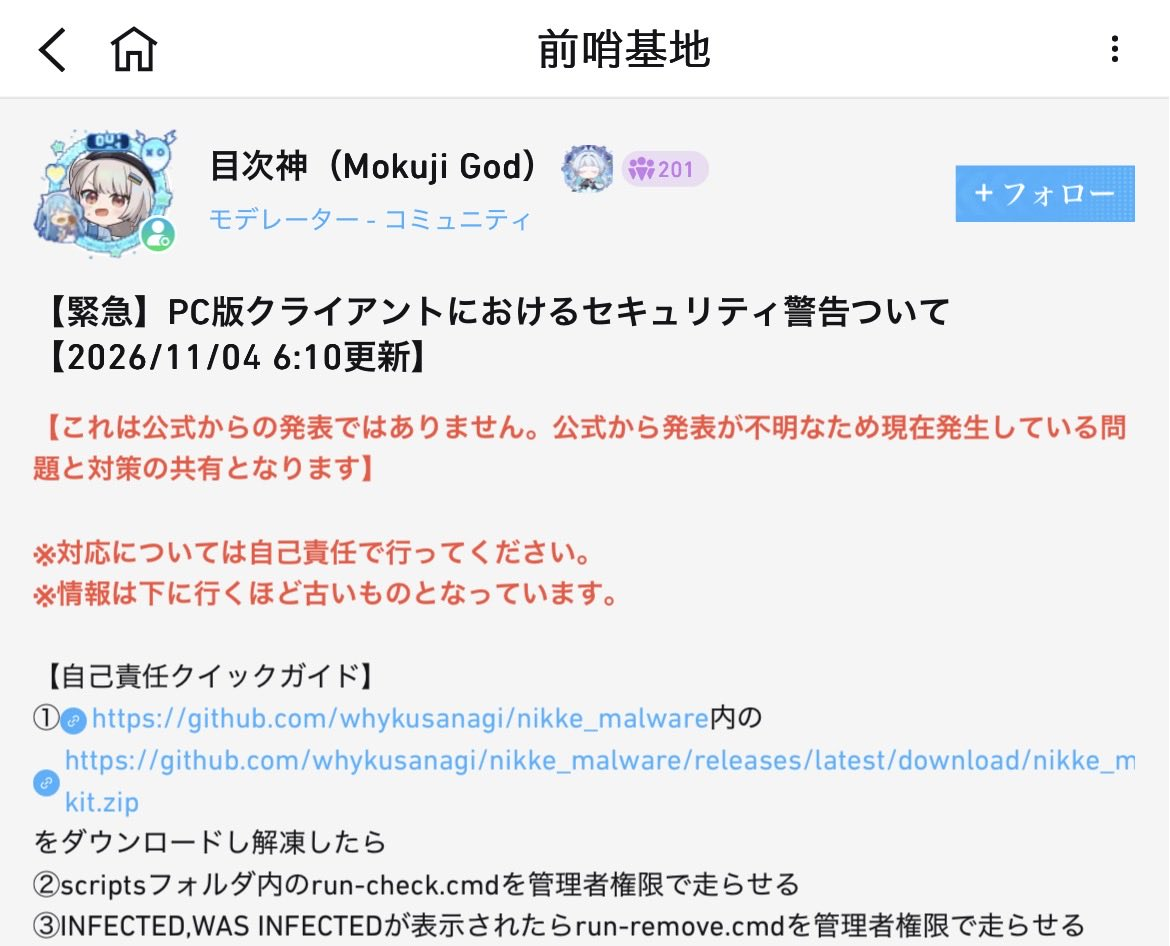
これは公式からの発表ではありません。公式から発表が不明なため現在発生している問題と対策の共有となります
"This is not an official announcement. Because there is no clear announcement from the official side, this is a share of the problem currently happening and what to do about it." That is a moderator, the closest thing a community has to staff, writing the empty chair into the first line of their post. If that 6:10 is Japan time, it went up about six hours before the first official word on X. Either way, it was being passed around on X by 23:48 GMT on 3 November, three and a half hours before NIKKE said anything at all. Once an official post finally went up, the moderator's was taken down. It had done its job: holding the chair until someone whose job it was turned up.
None of this was my job. I do not work for Shift Up, Level Infinite or Tencent. But in a live incident affecting players all over the world, somebody has to get out front. If nobody does, the space fills with disinformation, and then with the next attacker: fake "fix" tools carrying more malware, phishing dressed up as support, scams riding the panic. Silence is cover for all of it.
So I stepped in because nobody else had. Not to be thanked, and not because I wanted the chair. Because my own stuff was safe, I knew how to help, and the people whose job it was were still writing statements about inconvenience.
What they did get right, eventually
This is not a case that nothing was done. The files were replaced. The launcher now has a built-in check that offers to remove the stealer. The apology on the evening of 4 November says "as the operator, we take full responsibility for this failure". The website says to change passwords and revoke API keys. There is a route for reporting losses. An in-game mail went out to everyone.
Look at the shape, though. The website steps came about thirty hours after the files were fixed. They still never name crypto wallets or signing out of sessions. The recommended check runs through the PC launcher itself. And the in-game mail, the one message that reaches every player, was titled "Compensation". It apologises, lists 3,000 gems and ten recruit vouchers, and points elsewhere for everything that matters.
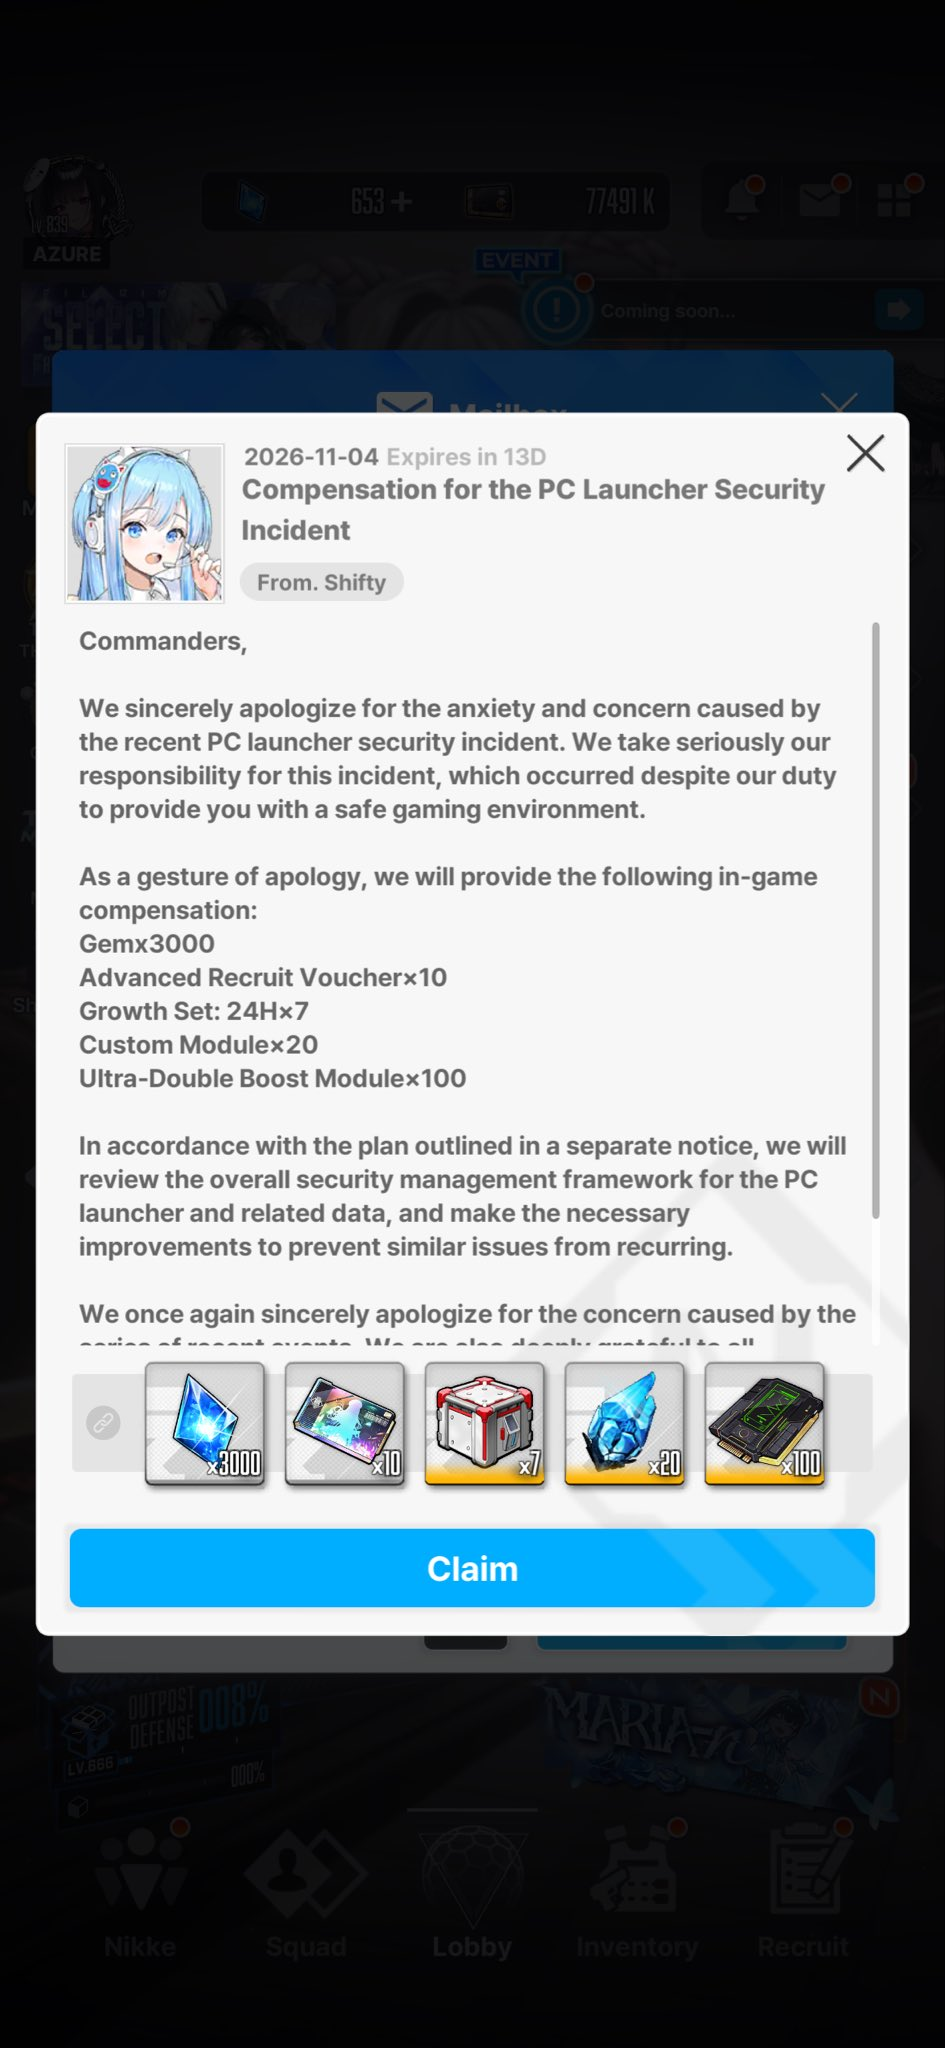
They had a message that reaches every player, and they used it for gems. Even players who had defended NIKKE and Shift Up since day one read the twenty pulls as an insult. Being sorry is not the same as being in charge.
Where I land
So here is where I land. Whose fault the breach was does not matter yet. Breaches happen to everyone. What matters is that when it happened, three companies shared one product and not one of them took the chair. They covered first, the way large companies do: minimise, manage, message, and apologise once the evidence is overwhelming. Even the CEO's step forward was a statement with no instruction in it.
The empty chair is the failure. It is why strangers on the internet, a moderator in Japan and a VTuber who never asked for it were the incident response. It is why good advice and wrong advice spread at the same speed. And it is why "it's not Shift Up, it's Level Infinite" is no defence at all. When nobody leads, it does not matter which of them was supposed to.
Still open. An in-game message that tells players what to do, not just what they get. Whether "crypto wallet" ever appears in an official statement. Anything from Tencent in its own name. Whether Level Infinite notifies EU regulators and players the way GDPR expects. The root cause on the CDN, and whether we get a real post-incident report. Whether the launcher starts verifying TLS certificates, which it currently does not. And whether Sky and Ada correct the registry claim, or leave it deleted.
Your demon onee-chan sat in the throne for them, onichan. It was never mine. Next time, one of them can sit in it 💜